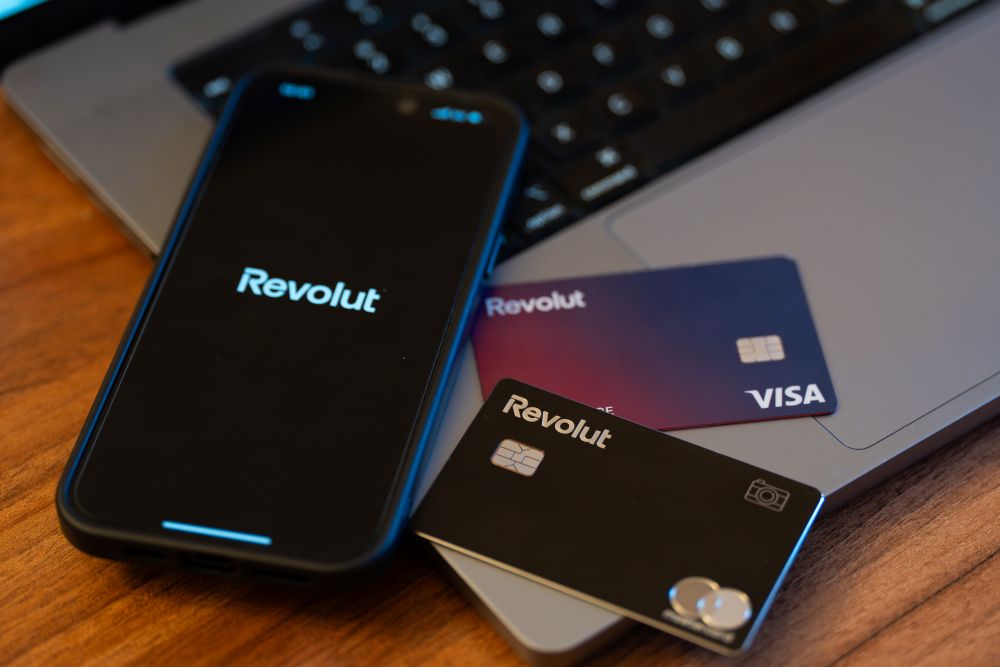

Irish Revolut customers are among those understood to have been affected after the fintech company mistakenly disclosed sensitive customer information to scammers posing as officials from a government agency.
The incident involved fraudsters using a legitimate government email domain to submit requests for customer information. Revolut said the requests appeared genuine because they passed technical domain authentication checks and were therefore processed as legitimate legal demands.
According to TechCrunch, which first reported the breach, the information potentially exposed included customers’ identities and contact details. This may have included dates of birth, postal and email addresses, telephone numbers and International Bank Account Numbers (IBANs). Copies of sensitive identity documents, including passports and driving licences, were also reportedly shared.
Revolut has declined to provide specific details about exactly what information was disclosed or how many customers were affected in Ireland or elsewhere. The company has instead described the number of impacted customers as “very limited” and said those affected have been contacted directly.
The incident has raised concerns among customers, particularly those whose accounts may already have experienced suspicious activity. One Dublin-based woman told the Irish Independent that her Revolut account had been hacked and that she was currently locked out. However, she could not confirm whether the incident was connected to the data disclosure or was an unrelated security issue.
She said the situation was particularly frustrating but added that she was fortunate to have an AIB current account, meaning she still had access to money while she was unable to use her Revolut account.
Revolut has stressed that the incident was not the result of a cyberattack on its core systems. “Our core infrastructure, databases, and customer accounts were not hacked,” the company said.
Instead, Revolut said the breach resulted from an “external impersonation scam” in which an unauthorised party used a genuine government agency email domain to submit fraudulent information requests.
The company said it acted immediately once the activity was identified, blocking the email address and notifying the relevant government agency, law enforcement authorities, data protection officials and financial regulators. It also insisted that customer funds and Revolut’s systems remained unaffected.
Revolut explained that financial institutions are legally required to respond to official requests from law enforcement and government bodies. Because the fraudulent requests appeared to originate from a verified government domain, they were initially treated as authentic and processed through normal compliance procedures.
The incident comes as Revolut continues its rapid expansion in Ireland. The company says it now has around 3.4 million Irish customers and more than 80 million customers worldwide. Its Irish lending operation has also surpassed €1bn, with approximately 300,000 credit facilities issued since the service launched four years ago.
The data incident comes at a significant time for Revolut, which has reportedly been considering a potential stock market listing that could value the company at up to $200bn. The fintech has also committed to investing $500m in the US and recently received conditional approval to operate as a national bank there.